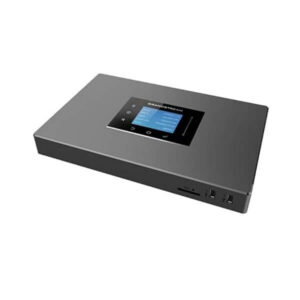
Fortinet FortiDDoS 1500F in Dubai, UAE
Fortinet FortiDDoS 1500F is designed for organizations that need dedicated, inline protection against volumetric, protocol, reflection, DNS, NTP, TCP, UDP, and application-layer denial-of-service activity. It sits in the traffic path without using IP or MAC addresses on its data interfaces, learns normal service behavior, evaluates traffic continuously, and can act automatically when attack patterns move outside learned baselines. For enterprises operating public services, customer portals, DNS infrastructure, e-commerce platforms, financial applications, hosting environments, or critical internet-facing systems, this appliance provides a focused DDoS control layer rather than asking a conventional firewall to absorb every flood event.
Request QuoteCheck UAE Availability
Quick Product Information
Fortinet
FortiDDoS 1500F / FDD-1500F
Inline DDoS protection appliance
2RU rack appliance
22 Gbps in the current ordering guide
27 Mpps in the current ordering guide
Four 10GE port pairs across SFP+ and fixed LC SR links
1 × 480 GB SSD
Dual redundant hot-swappable AC power supplies
Enterprise data centers, critical public services, hosting and service-provider networks
Configuration and supplier-status dependent
Confirm topology, optics, capacity, support term and deployment scope before quote
Decision Snapshot for Busy Security Buyers
This model is intended for buyers who already understand that a general firewall, load balancer, or ISP router is not a complete DDoS mitigation strategy. The key buying question is whether the appliance, link design, and support model match the organization’s actual internet exposure. Use the snapshot below to decide what must be checked before procurement moves forward.
Organizations running business-critical, internet-facing services where flood attacks could disrupt users, customers, transactions, communications, or hosted applications.
A dedicated mitigation layer that learns normal traffic and performs continuous packet inspection instead of relying only on static thresholds or traffic sampling.
Peak clean traffic, upstream capacity, number of protected services, fiber type, rack power, bypass design, HA expectation, and required service term.
Inline physical network designs where the DDoS appliance can be inserted on protected links and managed as a dedicated security control.
The standard 1500F uses short-range multimode 850 nm LC bypass interfaces; the 1500F-LR is a different orderable model for long-range single-mode requirements.
Share the network diagram and project requirement so FourTeck.com can help align the exact SKU, support option, delivery planning, and related infrastructure.
Product Overview
Distributed denial-of-service attacks are different from many conventional security events because the objective is often availability rather than intrusion. A flood can consume bandwidth, exhaust state tables, overload application resources, overwhelm DNS infrastructure, or force upstream devices to spend their capacity processing traffic that legitimate users never requested. For a business whose revenue, customer service, operational systems, or partner connectivity depends on public IP services, the result can be an outage even when no account is compromised and no malware crosses the perimeter.
Fortinet built the FortiDDoS family around dedicated traffic learning, full packet inspection, and rapid mitigation. The 1500F is positioned in the F-Series hardware range as a 2RU appliance with 10GE data interfaces, a 480 GB SSD, dual redundant hot-swappable AC power supplies, management interfaces, and built-in optical bypass on the fixed short-range LC port pairs. Fortinet documentation describes its data-path design as transparent: the inline traffic ports do not need IP or MAC addresses. This helps reduce the attack surface of the mitigation device itself and allows it to inspect traffic flowing between network segments without functioning as the routed termination point.
The system builds machine-learning baselines for normal network and service behavior. It monitors a large set of Layer 3, Layer 4, and Layer 7 parameters and compares current traffic against learned behavior. When a deviation is identified as an attack, mitigation can begin rapidly while the system continues evaluating other parameters for changing vectors. This matters for modern DDoS events, which may shift between SYN floods, UDP reflection, DNS abuse, invalid TCP states, protocol anomalies, and application-oriented patterns during the same incident.
For UAE organizations, the procurement decision should start with network architecture rather than simply the appliance model. Buyers should document the protected internet links, normal and peak traffic, public services, authoritative DNS role, upstream carrier handoffs, fiber type, rack location, power resilience, logging expectations, incident-response process, and whether a high-availability pair is required. FourTeck.com can use those details to help prepare a more accurate quotation and discuss how the appliance fits alongside existing firewalls, routers, load balancers, SIEM tools, and cloud or upstream mitigation services.
Key Business Benefits
Dedicated Availability Protection
A purpose-built DDoS appliance gives availability attacks their own control plane. That can reduce the pressure placed on firewalls, application servers, DNS systems, and other infrastructure that may otherwise be forced to process malicious floods before policy decisions can be made.
Continuous Traffic Learning
Machine-learning baselines help the appliance understand what normal service behavior looks like. For buyers, this supports a more adaptive approach than relying only on manual rate limits that can become outdated as legitimate traffic patterns change.
Full Packet Inspection
Fortinet positions FortiDDoS around inspection of all packets rather than sampled traffic. This is important during small-packet floods and rapidly changing multi-vector events where useful attack evidence may be lost if only a small traffic sample is evaluated.
Fast Mitigation Decisions
Fortinet documentation lists mitigation response from the first packet to less than one second for the 1500F. In business terms, faster detection and mitigation can reduce the time critical applications remain exposed to a flood before controls begin dropping malicious traffic.
Built-In Continuity Features
The appliance includes redundant hot-swappable AC power supplies and built-in optical bypass on designated 10GE LC SR port pairs. These design elements help network architects plan failure handling and maintenance with continuity in mind.
Deep DNS and Reflection Controls
DNS and NTP are frequent targets and amplifiers in DDoS activity. The 1500F includes advanced handling for DNS and NTP traffic and F-Series support for protocols such as DTLS, QUIC, and IKE, giving security teams more specific controls than broad protocol blocking.
Hybrid Mitigation Planning
On-premise mitigation remains limited by the physical capacity of the incoming link. Fortinet supports open attack signaling for integration with upstream or cloud mitigation workflows, helping organizations design a layered plan for attacks that threaten carrier bandwidth.
Product Highlights
Two pairs use 10GE SFP+ or GE SFP interfaces without integral bypass, while two pairs use fixed 10GE LC short-range multimode 850 nm interfaces with built-in optical bypass.
Fortinet’s data sheet lists 16 million simultaneous TCP connections and four million simultaneous sources for the 1500F, supporting busy public-facing environments when correctly sized.
The current ordering guide lists up to 16 Service Protection Profiles and up to 1,024 protected subnets per profile, useful for separating different services or business groups.
F-Series documentation covers DNS, NTP, DTLS, QUIC, and IKE controls, alongside traditional Layer 3 and Layer 4 flood protection and HTTP-oriented monitoring.
FortiDDoS provides graphs, attack logs, reports, alerts, SNMP, syslog, and RESTful API options so security teams can connect mitigation events to their wider monitoring and incident-response processes.
The protected traffic interfaces are designed without IP or MAC addresses in the data path, so the appliance can operate inline without becoming another routed address attackers can directly target.
A buyer should not select the appliance by throughput alone. Interface topology, optical media, upstream bandwidth, expected packet rates, simultaneous sessions, protected subnet design, response workflow, and high-availability planning all affect whether the 1500F is the right fit. Where a project requires long-range single-mode optical bypass, the 1500F-LR is a separate model and should not be treated as the same hardware SKU.
Technical Specifications
| Specification | FortiDDoS 1500F Detail | Buyer Relevance |
|---|---|---|
| Brand / Model | Fortinet FortiDDoS 1500F, SKU FDD-1500F | Confirm exact orderable SKU on quotation. |
| Product Type | Purpose-built inline DDoS protection appliance | Designed for dedicated attack detection and mitigation. |
| Form Factor | 2RU | Reserve rack space and verify airflow. |
| Enterprise Inspected Throughput | 22 Gbps in the current Fortinet ordering guide/data sheet profile | Size against legitimate traffic and expected attack conditions. |
| Inspected Packet Throughput | 27 Mpps | Important for small-packet floods. |
| SYN Flood Mitigation | Up to 21 Mpps in the current data sheet | Relevant for TCP service exposure. |
| Simultaneous TCP Connections | 16 million | Supports large state tables for public services. |
| Simultaneous Sources | 4 million | Useful for highly distributed attack-source scenarios. |
| Session Setup / Teardown | 726 kcps | Helps assess connection churn environments. |
| Latency | Less than 70 microseconds maximum/typical in data sheet | Important for inline placement in latency-sensitive networks. |
| Mitigation Response | First packet to less than 1 second | Reduces time to begin dropping attack traffic. |
| Advanced Mitigation | DNS, NTP, DTLS, QUIC, IKE | Useful for modern reflection and protocol attacks. |
| DNS / NTP Query Handling | 8M / 4M queries per second | Relevant when protecting authoritative DNS and NTP-facing services. |
| SFP+ Data Interfaces | 2 LAN + 2 WAN 10GE SFP+ / GE SFP interfaces | Transceiver speeds within port pairs must be planned correctly. |
| Built-In Bypass Interfaces | 2 LAN + 2 WAN fixed 10GE LC SR multimode 850 nm ports | Supports optical fail-open planning on designated links. |
| Management | 2 × GE RJ45 management ports; GUI, CLI, REST API, SNMP, syslog options | Integrate with operations and monitoring workflows. |
| Storage | 1 × 480 GB SSD | Supports local logs and system functions. |
| Power | Dual redundant hot-swappable AC; 100–240V AC, 50–60Hz | Plan dual feeds where infrastructure supports them. |
| Power Consumption | 333 W average / 433 W maximum | Include in rack power and cooling calculations. |
| Operating Temperature | 0°C to 40°C | Use conditioned data-room environments. |
| Dimensions | 88 × 438 × 580 mm | Check rack depth and cable clearance. |
| Weight | Approx. 19.8 kg | Plan safe rack installation and rail handling. |
| Support / Warranty | Based on selected FortiCare/service option and regional terms | Confirm service level and replacement terms before purchase. |
Choosing the correct configuration means looking beyond headline throughput. A 10 Gbps internet circuit can experience attacks that exceed the carrier link long before the appliance reaches its inspection limit. Equally, a lower-bandwidth service with extremely high packet-per-second rates may stress security infrastructure in a different way. Buyers should compare clean traffic, peak packet rate, expected simultaneous sessions, public subnet count, number of distinct protected applications, optical media, and the behavior of upstream routers and carriers. If the business requires a high-availability pair, that changes rack space, power feeds, optics, cabling, management addresses, and support quantities. FourTeck.com can review these variables before the quote so procurement receives a design-aligned bill of materials rather than a single appliance line item with missing dependencies.
Configuration and Buyer Guidance
A dedicated DDoS platform should be purchased as part of a network design, not as an isolated security box. The most useful first step is to document how traffic reaches the organization today. Identify every protected carrier link, the normal and peak bandwidth, current router and firewall topology, whether applications are behind load balancers or reverse proxies, which public IP ranges belong to the business, and whether authoritative DNS is hosted internally. This makes it possible to map Service Protection Profiles and determine where the appliance should sit inline.
Share average, peak and burst bandwidth plus packet-per-second observations if monitoring tools provide them.
List web applications, DNS, VPN gateways, APIs, mail services, gaming, hosted customer systems or other externally reachable assets.
Confirm multimode versus single-mode fiber, wavelength, transceiver types, port-pair speeds and whether integrated bypass is required.
Decide whether the appliance will be standalone or deployed as an active-passive pair for resilience and maintenance planning.
Document ISP or scrubbing-center options for attacks that can saturate the physical internet circuit before on-premise mitigation can help.
Choose the FortiCare term and response level based on how critical the protected services are and what replacement process the business expects.
Before requesting a formal quotation, provide FourTeck.com with the target model, quantity, deployment country, link speeds, preferred fiber type, rack environment, high-availability requirement, current DDoS platform if this is a replacement, and desired support term. If the project is replacing older FortiDDoS hardware, also share the current software release and any configuration export or documented protection-profile design that can be reviewed during migration planning. This information helps avoid buying the short-range model where long-range optics are required, underestimating rack and power requirements, or omitting support and integration items that become important after delivery.
Ideal Business Use Cases
Public Web and Digital Services
Organizations operating customer portals, online ordering, booking systems, API endpoints, public websites, payment-facing applications, or other revenue-linked services can use dedicated DDoS mitigation to protect availability when flood attacks are intended to make those services unreachable.
Data Center Internet Edge
Enterprise data centers with multiple public subnets and several externally reachable services can separate protection policies according to application groups, infrastructure roles, or business units. The 1500F’s profile and subnet scale make it relevant where traffic needs more granular treatment than a single global threshold.
Authoritative DNS Protection
Businesses that host their own authoritative DNS can benefit from specialized query and response inspection, reflection controls, source validation, and traffic learning. DNS availability is especially important because an outage can make many otherwise healthy applications appear unreachable.
Hosting and Managed Services
Hosting companies, colocation environments, and managed service providers may need to protect different customer-facing networks without treating all traffic identically. Service Protection Profiles allow more structured policy separation when the final design matches the provider’s customer and subnet model.
Financial and Transaction Platforms
Banks, payment services, exchanges, fintech platforms, and transaction-heavy businesses may treat internet availability as a critical control objective. Dedicated DDoS mitigation can complement existing firewall, application-security, fraud, and monitoring layers without replacing those controls.
Critical Multi-Site Enterprises
A group with public services concentrated in a primary data center can protect shared corporate infrastructure while still using cloud or carrier scrubbing for very large attacks. This hybrid planning is useful where a company wants local visibility but recognizes the physical limit of its incoming bandwidth.
The appliance is not a replacement for a next-generation firewall, web application firewall, endpoint protection platform, or upstream carrier capacity. Its role is narrower and more specialized: identify and mitigate denial-of-service traffic so legitimate traffic has a better chance of reaching the systems that process it. A strong architecture therefore places FortiDDoS within a layered design and clearly defines which system is responsible for routing, firewall policy, application-layer security, identity, logging, and upstream diversion.
FortiDDoS 1500F Machine-Learning Traffic Baselines
One of the core design ideas behind FortiDDoS is that DDoS protection should understand the normal behavior of each protected service rather than depend only on a fixed library of signatures. The appliance continuously learns traffic and resource patterns and develops adaptive thresholds across a large number of parameters. That matters because a traffic level that is normal for a public API may be abnormal for an internal-facing web portal, while a DNS service can have very different query and response behavior from an HTTPS application.
For IT and security teams, the practical value is more contextual detection. A static rate limit can be easy to configure but difficult to maintain. If it is too low, legitimate demand spikes can be blocked. If it is too high, an attacker may stay below the threshold while still stressing a vulnerable application. Adaptive baselines give the mitigation platform more context about direction, protocol, port, destination, source behavior, TCP state, DNS characteristics, and other factors. Fortinet also describes continuous attack evaluation, meaning the platform keeps reassessing conditions rather than treating the initial mitigation decision as permanent.
This does not eliminate the need for careful design. The learning period, service grouping, network changes, maintenance events, application launches, and traffic migrations should be communicated to the team responsible for DDoS operations. A major marketing campaign or platform migration can change legitimate behavior significantly, so the security operations process should include change awareness. Buyers should therefore consider not only appliance capacity but also who will own policy review, alert handling, reporting, and incident coordination after deployment.
FortiDDoS 1500F Inline Connectivity and Optical Bypass
Physical connectivity is one of the most important distinctions between the 1500F and alternative models. The appliance provides two protected port pairs through 10GE SFP+ interfaces that can also accept GE SFPs, plus two protected port pairs using fixed 10GE LC short-range multimode 850 nm interfaces with integrated optical bypass. Those fixed bypass links are not generic transceiver slots. The fiber type, distance, wavelength, patching, and connected equipment need to match the short-range design. Buyers who require long-range single-mode optical bypass should review the separately orderable 1500F-LR model instead.
Bypass matters because an inline security control sits directly in the path of business traffic. Fortinet’s hardware documentation supports fail-open behavior on the designated optical bypass ports, allowing the physical link to remain available under defined appliance failure or bypass conditions. Network architects still need to decide whether fail-open behavior is appropriate for their risk model, how routing and adjacent devices respond during a failure, and whether a high-availability FortiDDoS pair is also part of the design. Bypass is a continuity feature, not a substitute for a complete resilience plan.
Rack engineering should be completed before shipment. The appliance occupies 2RU, weighs about 19.8 kg, uses front-to-back airflow, and has dual redundant hot-swappable AC power supplies. The data sheet lists an average power consumption of 333 W and maximum of 433 W. Procurement teams should therefore confirm rack depth, rail requirements, power distribution, dual-feed availability, cooling, cable-management space, optical patch leads, and any spare transceivers needed for the non-bypass SFP+ ports. FourTeck.com can include these questions in the pre-quote discussion so the delivered hardware fits the intended data-room environment.
FortiDDoS 1500F DDoS Mitigation, DNS Protection and Operations
The most demanding DDoS incidents rarely stay inside a single protocol. A campaign may combine spoofed UDP reflection, SYN floods, abnormal TCP flags, fragmented traffic, DNS responses, high-rate application requests, and pulsed traffic that changes faster than a human analyst can manually build rules. FortiDDoS is designed to inspect and mitigate multiple vectors in parallel while continuing to evaluate traffic as the incident develops. The F-Series feature set also includes advanced monitoring for DTLS, QUIC, and IKE, protocols that are increasingly relevant in modern encrypted and real-time communications.
DNS deserves special attention because it is both a target and a potential reflection mechanism. Fortinet documents high-rate DNS query and response inspection and validation, including specific handling for unexpected or unmatched responses and other DNS anomalies. For an enterprise that hosts authoritative DNS, this can help distinguish normal query behavior from reflected or malformed traffic without simply blocking the entire protocol. Similar principles apply to NTP and other UDP-based services where broad blocking can protect infrastructure but disrupt legitimate users.
Operations after an event are also important. FortiDDoS includes attack logs, graphs, reports, alerting, SNMP, syslog, and RESTful API capabilities. These tools let security teams correlate DDoS events with firewall logs, application monitoring, carrier telemetry, SIEM data, and incident tickets. The platform also supports open signaling for hybrid mitigation. If an attack grows large enough to threaten the upstream circuit itself, an on-premise appliance cannot restore bandwidth that has already been saturated. A mature design therefore defines when local mitigation is sufficient and when the ISP or cloud scrubbing provider must be engaged.
What Should You Know Before Choosing This DDoS Platform?
The questions below reflect the way infrastructure teams, security leaders, procurement managers, consultants, and finance approvers evaluate a dedicated DDoS appliance. The answers focus on fit, capacity, physical connectivity, operational ownership, and purchasing details that should be resolved before a quotation is approved.
Who is the 1500F best suited for?
It is best suited to organizations with important internet-facing services and 10GE-oriented network designs that need a dedicated inline DDoS control. Typical buyers include enterprise data centers, hosting providers, financial platforms, digital-service businesses, and operators protecting public DNS or application infrastructure. Suitability still depends on actual traffic, packet rates, upstream bandwidth, and resilience requirements rather than company size alone.
How much traffic should the appliance be sized for?
Start with legitimate peak traffic, packet-per-second behavior, simultaneous sessions, and the capacity of every protected link. Fortinet’s current ordering guide lists 22 Gbps enterprise inspected throughput and 27 Mpps small-packet inspection for the 1500F. Those figures should be compared with the project topology, not treated as a guarantee that the appliance can solve an attack that has already saturated the ISP circuit.
Can it protect several public services with different traffic patterns?
Yes, the platform supports separate Service Protection Profiles so different service groups can be learned and protected according to their own behavior. The current ordering guide lists up to 16 profiles and up to 1,024 protected subnets per profile for this model. The design team should decide how to group firewalls, web services, DNS systems, and other public subnets before implementation.
Will the standard 1500F work with my existing fiber links?
It can fit many 10GE designs, but the exact optical media must be checked. Its built-in bypass ports use fixed short-range multimode 850 nm LC connectivity. The non-bypass pairs use SFP+ or GE SFP transceivers. If the project requires long-range single-mode bypass, review the separate 1500F-LR. Share fiber type, wavelength, distance, connector type, and adjacent device interfaces before ordering.
Does the appliance replace our firewall or web application firewall?
No. FortiDDoS has a specialized role focused on denial-of-service detection and mitigation. Your firewall still handles security policy, routing or VPN functions depending on design, while a web application firewall may provide application-specific controls. A layered architecture should define each product’s responsibility so DDoS mitigation complements rather than duplicates existing perimeter and application-security controls.
What should be checked when replacing an older DDoS appliance?
Document the existing link speeds, optics, bypass behavior, public subnets, service groups, high-availability design, software version, monitoring integration, and support process. Do not assume cabling or policy structures transfer directly. Migration should also account for baseline-learning time and any application changes since the older appliance was installed. A current network diagram and configuration summary are valuable inputs for the replacement plan.
Should we buy one appliance or an HA pair?
That depends on the organization’s availability target, maintenance process, rack design, and budget. Fortinet supports high availability across the FortiDDoS family. A pair adds resilience but also doubles hardware, power, rack, cabling, and support requirements. Buyers protecting mission-critical services should discuss failure scenarios and maintenance expectations before deciding whether standalone deployment meets the business continuity requirement.
Do we need optional reputation subscriptions for basic DDoS mitigation?
Fortinet’s ordering guide states that IP and Domain Reputation subscriptions are optional and are not required for enterprise DDoS mitigation. A buyer may still choose reputation services for specific policy objectives. The commercial quote should clearly separate hardware, FortiCare support, optional security services, and any professional deployment assistance so finance teams understand recurring versus one-time costs.
What information should we send FourTeck.com for an accurate quote?
Send the required model or target capacity, quantity, protected bandwidth, packet-rate data if available, public subnet count, service types, fiber media, rack location, power design, high-availability requirement, current appliance if replacing one, support term, destination country, and expected project timeline. A network diagram is especially useful because it reveals the interfaces and related items that a model-only request can miss.
Business Requirements to Match Before You Buy
For businesses that need dedicated attack mitigation
Choose a purpose-built platform when service availability requires a control that continuously inspects DDoS behavior instead of relying entirely on perimeter firewall resources. Confirm that the network can physically place the appliance inline.
For 10GE data-center links
The 1500F is designed around 10GE port pairs. Buyers should match actual SFP+, GE SFP, and fixed LC short-range interfaces to the connected routers or switches and verify media before the bill of materials is approved.
For teams protecting several service groups
Multiple Service Protection Profiles can help separate applications, infrastructure, and public subnets so each group is learned and monitored according to its own behavior rather than sharing one broad policy.
For projects that need continuity planning
Built-in optical bypass and redundant hot-swappable AC power support resilient designs, but buyers should still determine whether HA appliances, dual power feeds, carrier diversity, and upstream scrubbing are required.
For organizations replacing older protection
A refresh should include policy mapping, cable and optic review, software compatibility, log integration, support planning, and a controlled baseline-learning period. The replacement decision is broader than comparing throughput numbers.
For procurement teams comparing total project cost
Separate appliance hardware, FortiCare, optional reputation services, professional deployment, optics, patching, rack work, HA quantity, and recurring operational services. This gives finance a more accurate lifecycle view than a hardware-only price.
What Buyers Should Check Before Purchase
A model name is only the beginning of a DDoS project. Before procurement, the organization should verify the physical topology, service design, operational ownership, and commercial scope. This reduces the risk of receiving the right appliance but the wrong optics, support level, deployment assumption, or resilience plan.
Configuration Fit
Confirm traffic bandwidth, packets per second, session scale, protected subnet count, service grouping, and whether 22 Gbps / 27 Mpps documented enterprise performance aligns with the deployment profile. Where requirements exceed the model, evaluate a larger FortiDDoS platform rather than relying on optimistic headroom.
Compatibility Check
Review router and switch interfaces, transceiver type, multimode versus single-mode fiber, rack depth, power distribution, monitoring systems, syslog destinations, authentication services, and any high-availability connections. Port-pair speeds and media should be consistent with the Fortinet hardware guide.
Availability and Warranty
Availability can change with supplier status, country, quantity, support bundle, and project timing. Warranty and replacement expectations should be tied to the selected FortiCare/service option rather than assumed from the hardware name. Request current commercial terms before approval.
Quote Preparation
Send a network diagram, model quantity, fiber information, carrier links, protected services, expected support term, deployment location, HA requirement, and target project date. For replacement projects, include the older model and current policy structure so migration dependencies can be identified early.
Also consider the boundary between on-premise and upstream mitigation. If an attack is larger than the incoming circuit, local hardware cannot recover bandwidth that the carrier has already filled with malicious traffic. Ask the ISP what DDoS services, BGP signaling, diversion, FlowSpec, or cloud-scrubbing integrations are available. Then define an incident runbook covering alert ownership, escalation thresholds, carrier contacts, log review, and business communication. Long-term operational readiness often matters as much as the appliance specification.
UAE Availability and Service Support
FourTeck.com supports Fortinet enterprise-security inquiries across Dubai and the wider UAE with assistance for model review, quote preparation, configuration discussion, delivery coordination, and warranty guidance. Availability for FortiDDoS hardware can vary because this is an enterprise appliance whose supply may depend on the exact SKU, support term, optical variant, project quantity, regional supplier status, and required delivery schedule. FourTeck therefore recommends confirming the live commercial position before procurement teams lock a project date.
For a useful availability check, share whether you require the standard short-range 1500F or the long-range 1500F-LR, the number of appliances, whether the deployment is standalone or high availability, and the preferred FortiCare term. Include any optional IP or Domain Reputation services separately so the quotation clearly distinguishes required hardware and support from optional services. If the system will be installed into an existing rack, also provide the site’s fiber media and power design.
Delivery coordination is handled according to the confirmed order, destination, supplier status, and project conditions. FourTeck.com does not assume that a particular configuration is immediately available. For warranty planning, buyers should verify the FortiCare level, replacement process, response target, and regional coverage shown on the final quotation. These details are especially important when the appliance protects customer-facing or operationally critical services.
Dubai, Abu Dhabi, Sharjah and Ajman Coverage
Businesses in Dubai, Abu Dhabi, Sharjah, Ajman, and other UAE locations can contact FourTeck.com for product availability, configuration guidance, and quotation support. A Dubai data center may need to confirm 10GE optical connectivity and carrier handoff, while an Abu Dhabi enterprise may prioritize documentation, support terms, and resilient deployment for a regulated environment. A Sharjah hosting or industrial organization may focus on public-service continuity, and an Ajman business may be coordinating protection for a centralized application platform. FourTeck uses the actual project requirement—not the city name—to review the hardware, service scope, delivery conditions, and related infrastructure. Share the destination, rack environment, link design, quantity, and target timeline so the commercial proposal reflects the real deployment.
GCC and Africa Availability
FourTeck.com also supports business technology inquiries for selected GCC and Africa projects where organizations need a common procurement contact for enterprise security infrastructure. Requests may involve Saudi Arabia, Qatar, Oman, Kuwait, Bahrain, Kenya, Uganda, and other regional destinations. Availability, support coverage, import conditions, delivery method, warranty handling, and implementation scope can differ by country, so the exact commercial path should be confirmed for each project instead of assuming UAE terms apply everywhere.
Regional buyers often standardize the same security architecture across several data centers or service locations. In that situation, send one consolidated requirement showing country, quantity, required model, optical variant, support term, rack readiness, and whether all locations will use the same network design. FourTeck can then help structure the inquiry and identify where local delivery or support conditions need to be treated separately. Organizations can also use FourTeck Kuwait, FourTeck Kenya, FourTeck Uganda, and FourTeck Africa for regional inquiry channels where relevant.
For multinational projects, also ask how vendor support entitlement, replacement service, and device registration will be handled in each destination. Enterprise DDoS hardware is often part of a longer operational lifecycle, so these support details should be understood before shipment rather than after an incident.
Other FourTeck.com Security Options to Consider
A dedicated DDoS appliance usually sits beside firewalls, monitoring systems, application-security controls, and carrier services. The products below are not direct substitutes for the 1500F, but they can be relevant when a wider Fortinet security architecture is being reviewed. Final model selection should be based on each product’s role and the performance needed for that role.
FortiGate 121G
Useful for organizations that also need a rack-mounted Fortinet next-generation firewall with local SSD storage and 10GE connectivity at the enterprise edge.
FortiGate 120G
A related Fortinet firewall option for businesses planning secure internet access, VPN, SD-WAN, application control, and threat inspection alongside specialist DDoS protection.
FortiGate 90G
Suitable for branch and office security projects that need a smaller Fortinet NGFW while central public services may be protected separately by data-center DDoS infrastructure.
FortiGate 101F
An established Fortinet firewall option for medium and enterprise branch environments where local logging, VPN, and secure edge policy are required.
Fortinet Firewall Solutions
Use FourTeck’s Fortinet firewall overview when the project also needs model sizing, license planning, VPN, branch security, or Secure SD-WAN discussions.
For a direct FortiDDoS capacity comparison, organizations should also review Fortinet’s smaller 200F and larger 2000F/3000G platforms through the active vendor documentation and current order guide. FourTeck.com can help discuss which model tier better matches the project after bandwidth, packet rate, interface, and protected-subnet requirements are shared.
Why Buyers Choose FourTeck.com for Enterprise Security Projects
Enterprise cybersecurity procurement is rarely successful when the purchasing conversation stops at a model number. FourTeck.com focuses on the practical information that helps the buyer move from a requirement to a usable quotation. For DDoS projects, that means discussing bandwidth, traffic profile, protected applications, optics, rack environment, resilience, support coverage, and regional delivery needs before finalizing the commercial scope.
Coordination for enterprise hardware, related components, project quantities, and delivery requirements.
Pre-sales discussion to help clarify model, optical variant, HA requirement, and support scope before order.
Structured commercial proposals based on the exact requested configuration rather than generic model-only pricing.
Planning based on confirmed supplier status, destination, quantity, and project requirements.
Help reviewing FortiCare and service terms so support expectations are understood before purchase.
Assistance for multi-country business requirements where procurement, delivery, and support may differ by destination.
FourTeck can also help buyers identify related infrastructure that may be missing from an initial request, such as optics, patch leads, rack power planning, compatible firewalls, logging platforms, or alternate models. The objective is to reduce procurement surprises. If the exact requested model is not the best fit, the discussion can shift toward a more suitable FortiDDoS capacity tier or a different optical variant instead of forcing the original model into an unsuitable topology.
For consultants and tender teams, FourTeck can work from a bill of quantities or technical requirement and highlight where more information is needed for a clean quotation. For IT managers, sharing a network diagram and traffic metrics usually produces a better result than sending only a product name. For finance approvers, separating hardware, support, optional services, and deployment scope makes recurring costs easier to understand and compare.
Frequently Asked Questions
What is FortiDDoS 1500F used for?
It is a dedicated inline appliance for detecting and mitigating distributed denial-of-service attacks against networks and public services. It learns normal traffic patterns, inspects packets across multiple layers, and can automatically respond to attack traffic. It is commonly considered for enterprise data centers, hosting environments, public DNS, online platforms, and other infrastructures where service availability is a critical business requirement.
What throughput does the 1500F support?
Fortinet’s current ordering guide and downloadable data sheet list 22 Gbps enterprise inspected throughput and 27 Mpps inspected packet throughput for the 1500F. Fortinet’s public model overview may show a different inspected-rate figure, so buyers should confirm the active vendor specification and test profile on the final quotation. Real deployment sizing must also consider packet rate, sessions, service mix, and upstream bandwidth.
Does the appliance include optical bypass?
Yes, designated fixed 10GE LC short-range multimode 850 nm port pairs include built-in optical bypass. The SFP+/SFP port pairs do not provide the same integrated bypass function. Because the standard 1500F is short-range on those fixed ports, buyers needing long-range single-mode bypass should review the separate 1500F-LR model and confirm the fiber design before ordering.
Can FourTeck.com help with configuration planning?
Yes. FourTeck.com can discuss model fit, quantity, short-range versus long-range optical requirements, HA expectations, support term, rack requirements, and the information needed for a complete quotation. For the best pre-sales review, provide a network diagram, protected bandwidth, public subnets, service types, current appliances, fiber media, and destination so the discussion can focus on the actual deployment.
Is FortiDDoS 1500F available in Dubai and the UAE?
FourTeck.com supports Dubai and UAE quotation and availability inquiries, but live supply depends on the exact SKU, quantity, FortiCare option, supplier status, and project timing. Enterprise DDoS hardware should be checked at the time of purchase rather than assumed to be immediately available. Share the required model, quantity, delivery location, and support term to request a current commercial update.
Does FortiDDoS replace upstream cloud scrubbing?
Not necessarily. An on-premise appliance can mitigate attacks up to the limits of the incoming network path, but it cannot restore bandwidth once a larger attack has already saturated the carrier circuit. Fortinet supports open signaling for hybrid mitigation designs, allowing organizations to combine local inspection and visibility with upstream or cloud services when attack volume threatens external link capacity.
Are reputation subscriptions mandatory?
Fortinet’s current ordering guide indicates that IP and Domain Reputation subscriptions are optional and not required for enterprise DDoS mitigation. They may still be useful for specific policy or intelligence requirements. Procurement teams should ask for the quotation to separate hardware, FortiCare, optional subscriptions, and any deployment services so recurring items are clear before approval.
What warranty or support should a buyer select?
The appropriate FortiCare or service level depends on the criticality of the protected services, acceptable outage duration, replacement expectations, and regional support conditions. Buyers should not assume all service levels provide the same response or hardware-replacement terms. FourTeck.com can help review the requested term and include the selected support scope in the quotation for commercial confirmation.
How do I request a FortiDDoS quotation?
Use the FourTeck.com contact page and provide the model, quantity, deployment location, protected link speeds, fiber media, HA requirement, support term, and project timeline. If possible, attach a network diagram and traffic information. These details help FourTeck prepare a quotation that reflects the correct appliance variant, support choice, and related project requirements instead of quoting only the hardware name.
Need Help Planning a FortiDDoS Deployment?
FourTeck.com can help you review the product variant, protected bandwidth, fiber requirements, high-availability design, FortiCare term, availability, warranty guidance, and delivery requirements for your business. Share your network diagram and project scope to start a configuration-focused quotation.